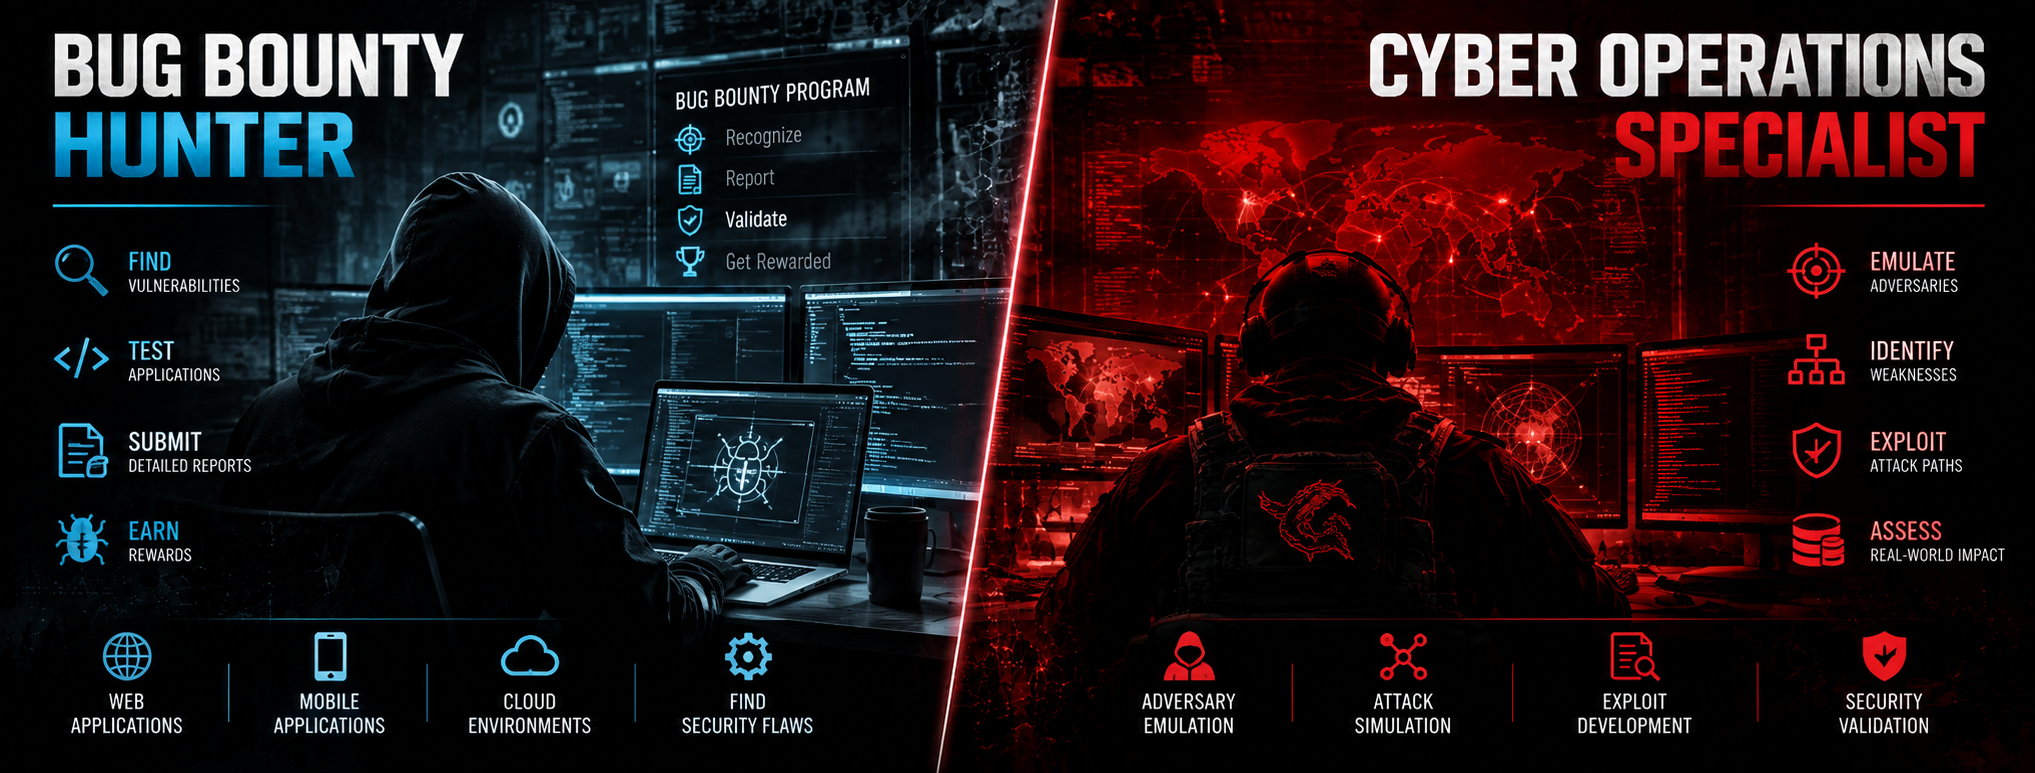
Bug bounty hunting finds the weakness, cyber operations go beyond discovery to understand, simulate, and validate how that weakness can shape the broader attack path.
Key Distinctions
Understanding the differences between Cyber Operations and Bug Bounty Hunting is essential because, although both contribute to cybersecurity, they differ in scope, objectives, methodologies, and engagement models. Recognizing this distinction helps organizations select the appropriate approach based on their specific security requirements.
Bug Bounty Hunters
Bug Bounty Hunters are security researchers who identify and responsibly disclose vulnerabilities in applications, websites, APIs, and other digital assets within an authorized bug bounty program. Their primary focus is vulnerability discovery, validation, documentation, and responsible reporting, typically in exchange for recognition, rewards, or monetary bounties.
- Methodology: Find and report bugs.
- Priority: Bugs and rewards.
- Scope: Defined and limited by the bug bounty program.
- Objective: First valid report wins.
- Log Clearing: Generally out of scope.
Log manipulation is generally outside standard bug bounty scope, while Blue Team detection and evasion testing is typically excluded unless explicitly authorized by the program
Cyber Operation Specialists
Cyber Operations are authorized, objective-driven activities designed to simulate or conduct controlled actions against a target environment to assess security, achieve defined operational objectives, and understand the potential consequences of a compromise
- Methodology: Simulate adversary behavior.
- Priority: Mission objectives and impact.
- Scope: Authorized target environment.
- Objective: Achieve defined operational goals.
- Log Clearing: Can be within scope as part of authorized operational objectives
Blue Team detection and evasion testing is a mandatory component of cyber operations, subject to the authorized Rules of Engagement. Detection testing, evasion assessment, and authorized log-management
Choose Your Approach:
Choose a career path that aligns with your skills, interests, and professional goals. Build your expertise around the cybersecurity domain that best matches your career aspirations. Whether you pursue Bug Bounty Hunting or Cyber Operations, your goals can shape your path forward.